
Config Sync is a GitOps service included with Google Kubernetes Engine (GKE) that automatically syncs configurations and policies across your Kubernetes clusters from a central source of truth, such as a Git repository. Automated syncing helps you centrally manage fleets of clusters, prevent configuration drift, and improve stability and security for both platform and application teams.
This document is for Operators who want to centralize configuration management for their teams.
Benefits of Config Sync
Config Sync provides the following key GitOps advantages for managing your Kubernetes clusters:
- Consistency across environments: By using a central source of truth like a Git repository, you can ensure that your cluster configurations and policies remain stable and consistent across all your environments.
- Automated reconciliation: Config Sync continuously monitors your source of truth and automatically reconciles the state of your clusters to match it, preventing configuration drift and saving manual effort.
- Version-controlled configuration: Storing your Kubernetes manifests in Git lets you leverage standard version-control workflows, including peer reviews, audit trails, and easy rollbacks.
How Config Sync works
Config Sync continuously monitors a central source of truth and automatically reconciles the state of your clusters to match it. You can use a Git repository, OCI image, or Helm chart as your source of truth.
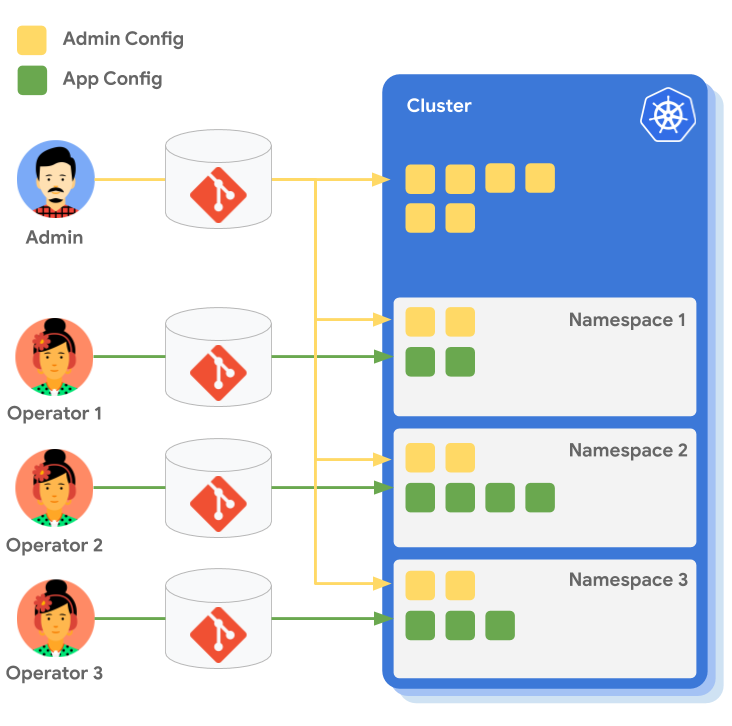
The following diagram shows an overview of how a platform administrator can manage central policies while three application operators manage their own namespace configurations. The namespaces all have the same admin configuration, but each namespace has a different application configuration.
Configuring clusters
Config Sync lets you create a common set of configuration and policies and consistently apply them across registered and connected clusters from a single source of truth.
Instead of repeatedly running the kubectl apply command manually, you can
orchestrate configuration changes across fleets of clusters.
Configuring namespaces
You can use Config Sync to provision and manage Kubernetes namespaces with namespace-scoped policies, such as RBAC roles. These policies can help you implement and manage multi-tenancy within your clusters, letting application teams to manage their own configurations safely.